The Soft Skills That Companies Actually Pay For in a Zero-Day Crisis
On March 2, 2021, Microsoft released emergency patches for four critical zero-day vulnerabilities in Exchange Server. Within hours, every serious organization’s incident response team was in crisis mode. By March 9, CISA reported that over 30,000 U.S. organizations had been compromised, including government agencies, schools, hospitals, and Fortune 500 companies. The attacks came from Hafnium, a Chinese state-sponsored group, and the exploitation was happening in real time across the internet.
If you were working in IT during those first frantic weeks, you know what the real bottleneck wasn’t. It wasn’t technical knowledge. It was communication. It was the ability to stand in front of stressed executives and explain what “SSRF vulnerability” and “web shell” actually meant for the business. It was the skill to coordinate between security teams, infrastructure teams, and leadership when everyone wanted answers and nobody had them yet. The IT professionals who excelled during ProxyLogon weren’t the ones who knew Exchange Server best. They were the ones who could think clearly under pressure, explain complicated things in simple terms, and keep everyone aligned when the situation was changing by the hour.
That’s what separates the mid-level technicians from the professionals who advance into leadership and command significantly higher salaries.
When Expertise Isn’t Enough
The ProxyLogon incident crystallized something that’s been true in IT for years but rarely discussed openly: technical skills are table stakes. Once you’re past entry level, knowing how to patch a vulnerability or interpret an IIS log isn’t a differentiator anymore. The field is full of people who can do that. What companies actually struggle to find are people who can do it while translating that work for non-technical stakeholders, staying calm when the executive team is panicking, and making decisions with incomplete information.
During the ProxyLogon response, every organization needed someone to answer these questions:
- What exactly did these attackers do to our systems?
- How many users were affected?
- What’s the real business impact?
- When will we be fully remediated?
A junior security analyst can tell you the CVE numbers. A mid-level IT professional can figure out the technical remediation path. But the IT leader who gets promoted and gets the raise is the one who walks into the board meeting and explains, in terms the CEO understands, why the company needs to drop everything for two weeks to patch every Exchange Server.
Communication Is the Real Skill Under Pressure
Think about what happened during ProxyLogon from the moment your organization learned about the vulnerabilities. Your team probably split into two camps: the engineers diving into technical response, and the people frantically trying to figure out what to tell the rest of the organization.
Those two jobs require completely different skills, and both are essential. But the second one is what managers notice.
If you’re the person who can draft an internal communication that explains the situation without minimizing it, that gives people a clear timeline for what to expect, and that doesn’t trigger panic, you’ve just created enormous value. You’ve freed up your technical team to focus on remediation instead of having to repeat the same explanation thirty times. You’ve kept the organization functional instead of letting fear paralyze operations. You’ve made your managers’ lives significantly easier.
And if you’re the one who can run the incident command structure, coordinate between teams that don’t usually work together, and make sure the right information reaches the right people at the right time, you’ve just demonstrated the exact skills that come with director and VP compensation bands.
The hard truth: most IT professionals never develop these skills. They stay technical. They get better at their specialization. But they never learn to operate as part of a coordinated response system. And that’s why they plateau.
Incident Response Is a Team Sport
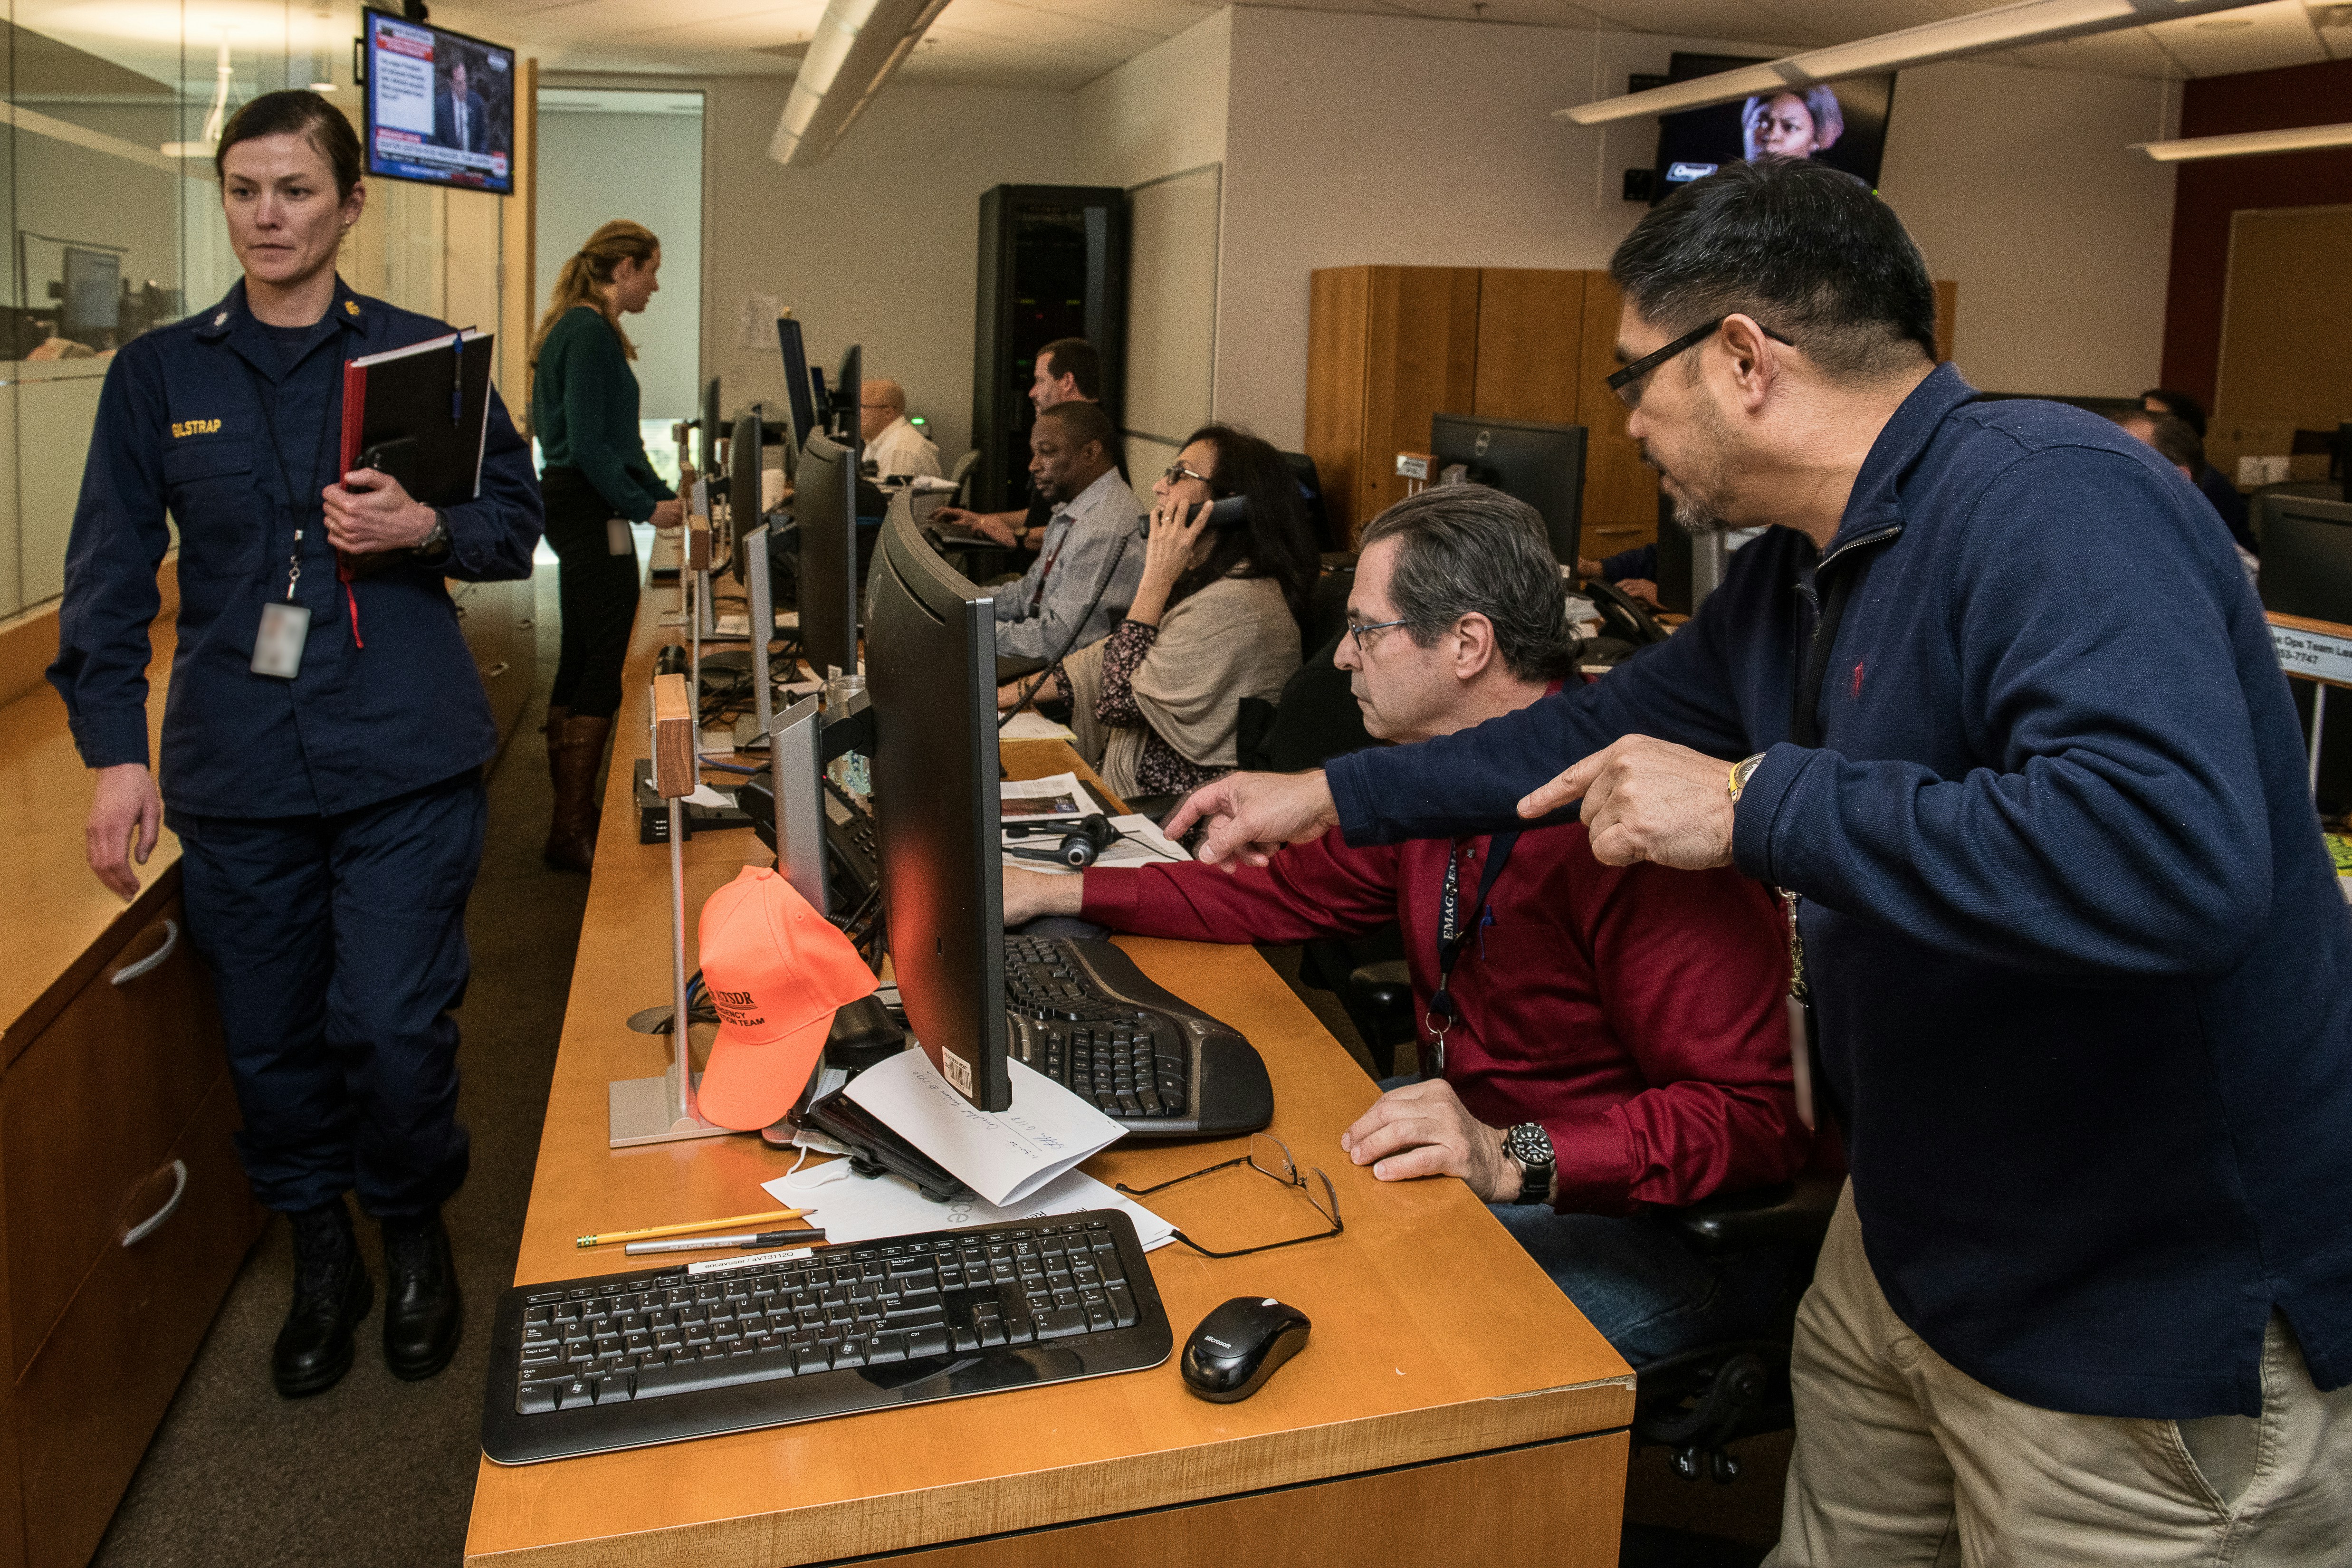
ProxyLogon required responses from security teams, systems administrators, network engineers, database administrators, and often external incident response firms. When you have that many people working on an urgent problem with incomplete information, everything breaks down unless someone is explicitly managing the coordination.
That person needs to understand the technical issues well enough to ask smart questions and catch missed details. But they also need to understand project management, resource allocation, and team dynamics. They need to know when the security team has what it needs and when they’re being asked to do the impossible. They need to speak both “engineer” and “executive” fluently.
If you’re that person in your organization, you’re worth more money. Full stop. Organizations that have gone through a major incident and come out the other side understand this viscerally. They’ve felt what it’s like to have clarity and coordination, and they’ve felt what it’s like to have chaos and finger-pointing. They’ll pay to keep you around.
The Exchange Server breaches in March 2021 weren’t unique. They were just the incident that made this dynamic visible. But it applies to every breach, every system outage, every infrastructure crisis. The companies that respond fastest and with the least organizational disruption aren’t the ones with the smartest engineers. They’re the ones with the best communicators running the response.
Why This Matters For Your Career Right Now
If you’re a mid-level IT professional reading this, and you’re thinking about what skills to develop, here’s my honest assessment: you can become incrementally better at your technical specialty, or you can become dramatically more valuable to your organization by developing crisis communication and coordination skills.
The first path gives you modest raises over time. The second path can accelerate you into management, specialist roles, or senior individual contributor positions that command significantly higher compensation.
ProxyLogon happened because of technical vulnerabilities, but the organizations that handled it best, the teams that earned trust and advanced in their careers because of their response, were the ones that managed the human side of the crisis. They were clear. They were honest. They were coordinated. They didn’t have all the answers, but they made sure everyone knew what the answer-finding process looked like and when to expect updates.
If you haven’t been tested by a major incident yet, this is hard to visualize. But if you have been through one, you know exactly what I’m talking about. You’ve seen the person who kept everyone aligned. You’ve seen the trust that builds around someone who can explain a technical nightmare in words that people actually understand. That’s not just valuable. That’s the kind of thing companies promote and pay for.
The next zero-day crisis is coming. It might be in your organization. When it does, the soft skills you develop now will determine whether you’re just another engineer managing tickets, or the person running the room.
Related reading on IT Atlas:
The ProxyLogon incident echoed patterns we saw months earlier with the SolarWinds breach, where supply chain compromise made organizations rethink their entire security posture. And the lessons we drew from what 2020 taught us about working in IT underscored how crisis response demands more than technical knowledge; it demands human skills in an industry that’s traditionally undervalued them.